

Hidden primary
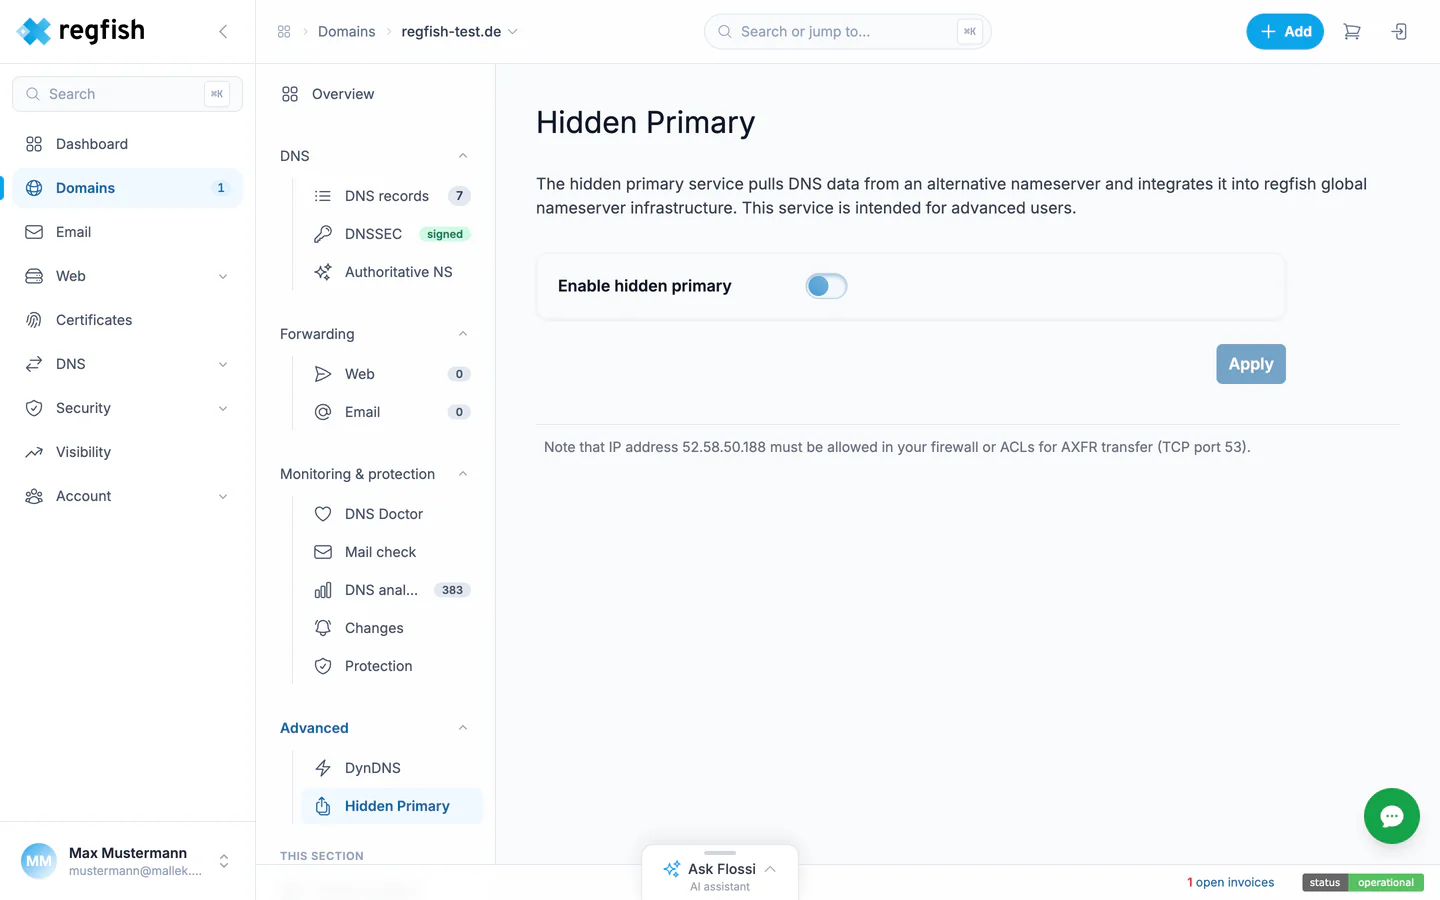
With a hidden primary you maintain the zone on your own nameserver, but the regfish nameservers stay in charge facing the world. regfish fetches the zone data from your server and distributes it over its own anycast infrastructure. The page itself calls the service one for advanced users, and that is accurate.
Where to find it
Section titled “Where to find it”Domains → your domain → Advanced → Hidden primary, direct address:
dash.regfish.com/my/domains/<tld>/<sld>/hpns
How it works
Section titled “How it works”Once activated, regfish fetches the zone from your nameserver via AXFR zone transfer. Your firewall has to allow the fetch address named on the page on TCP port 53; without that clearance no transfer happens.
From then on the zone is maintained on your server. The DNS records in the dash are no longer the source.
How it differs from delegation
Section titled “How it differs from delegation”| Authoritative NS | Hidden primary | |
|---|---|---|
| Who answers to the world | Your nameservers | The regfish nameservers |
| Where the zone is maintained | On your servers | On your primary |
| regfish anycast and DDoS shielding | No | Yes |
So the hidden primary is the way to combine your own zone management with the resilience of the regfish infrastructure.